Continuous Managed Detection & Response (MDR) Platform
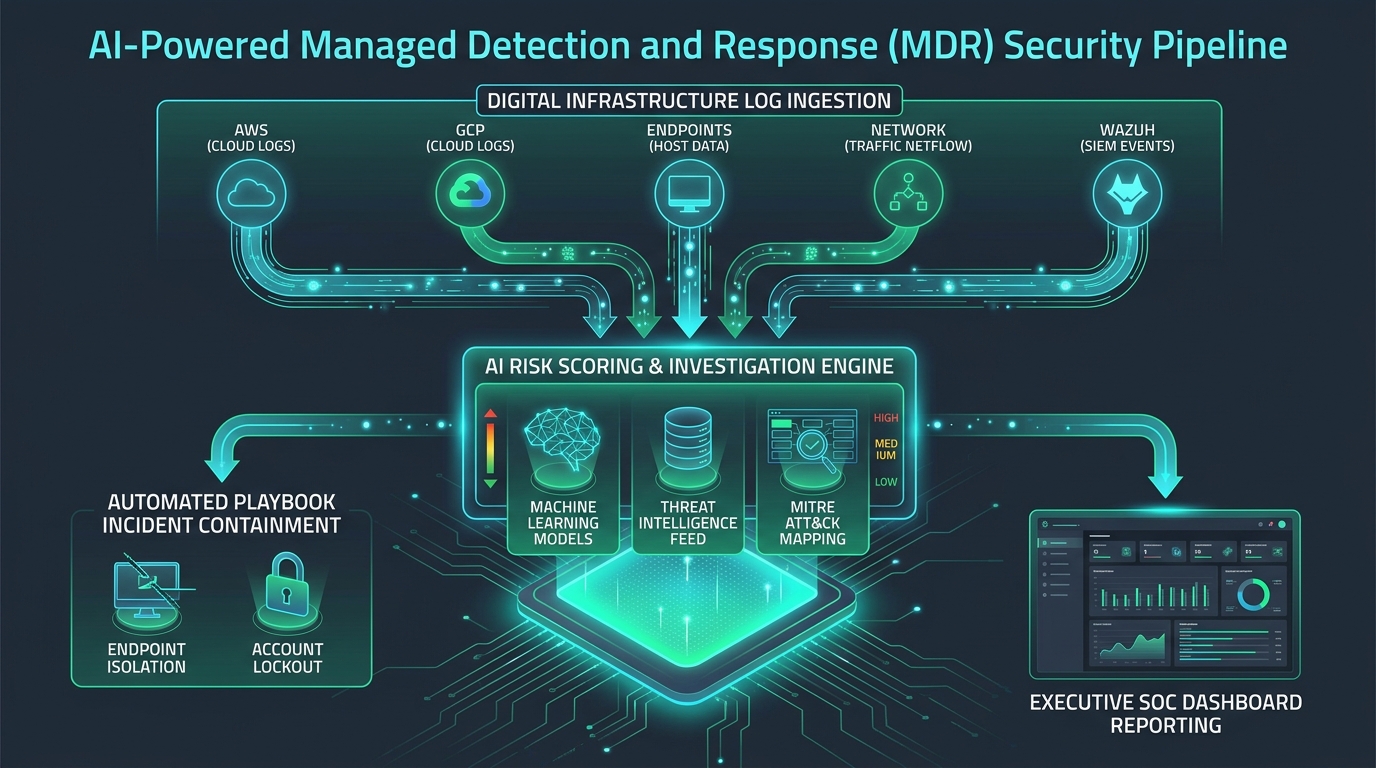
Defend your hybrid cloud and on-premise infrastructure with around-the-clock Security Operations Center (SOC) monitoring. Powered by automated multi-cloud log telemetry, AI risk scoring, and sub-4-minute incident containment.
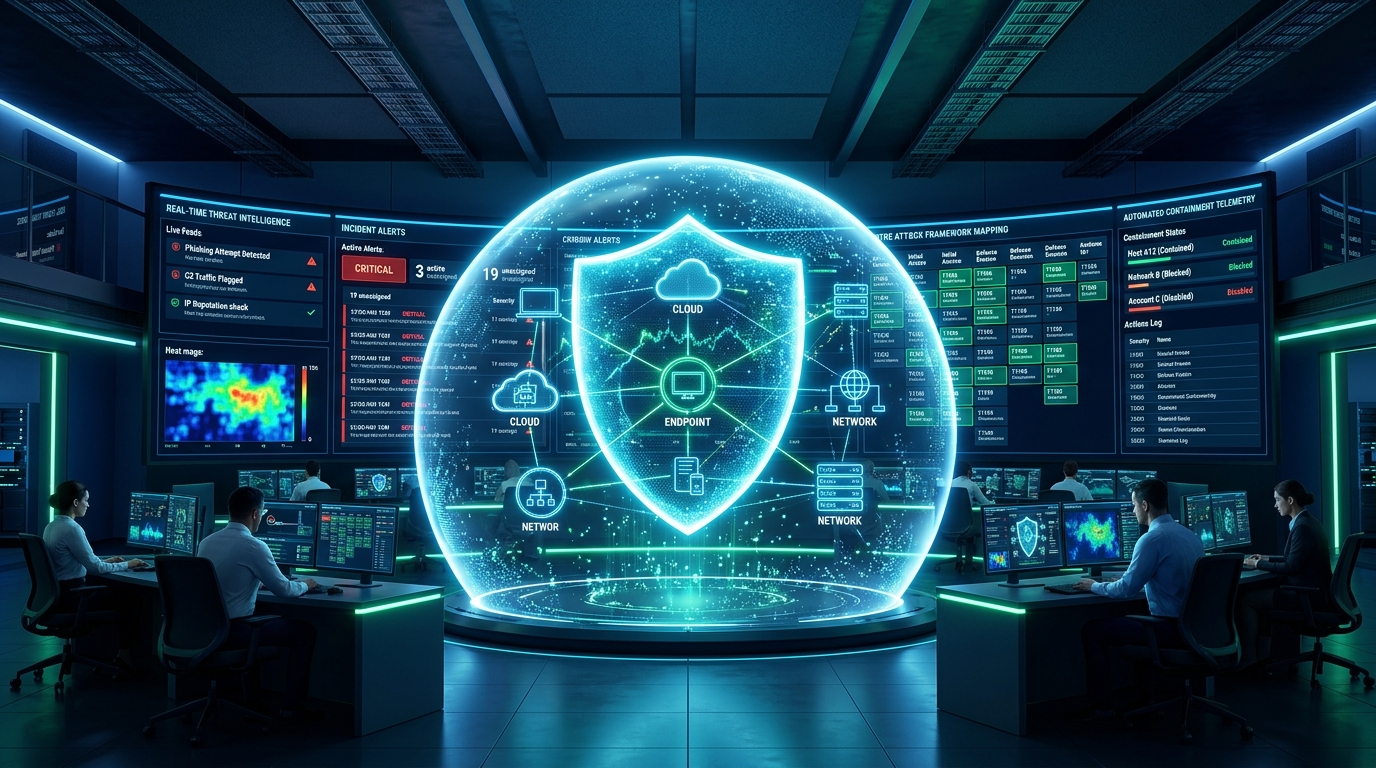
Complete Visibility & Automated Threat Eradication
Modern cyber attacks bypass traditional signature antiviruses. Our MDR pipeline pairs AI anomaly detection with offensive-security trained SOC analysts.
Multi-Source Telemetry Ingestion
Unified ingestion across AWS CloudTrail, Google Cloud Audit, Microsoft Sentinel, Wazuh agents, Active Directory, and perimeter firewalls into a centralized high-speed data lake.
AI Anomaly Scoring (0-100)
Neural risk scoring dynamically correlates disparate log signals, eliminating 90%+ of false positive alert fatigue and surfacing true critical indicators of compromise (IoCs).
Automated Containment Playbooks
Instant automated response actions: network host isolation, malicious IP perimeter blocking, active user session revocation, and process termination executed within seconds of breach detection.
MITRE ATT&CK Framework Alignment
Every detected incident is classified against standard MITRE tactics and techniques (Privilege Escalation, Lateral Movement, Exfiltration), ensuring systematic defense verification.
Proactive Threat Hunting
Our defensive analysts conduct continuous, hypothesis-driven threat hunts across dark web telemetry, zero-day intelligence feeds, and unmanaged perimeter assets.
NDPR, GDPR & ISO 27001 Reporting
Audit-ready executive compliance reporting detailing security posture, patch management, threat trends, and regulatory adherence across all company subsidiaries.
Traditional Antivirus vs. Legacy MSSP vs. Techline MDR
Why reactive security fails against modern ransomware and advanced persistent threats (APTs).
| Evaluation Factor | Traditional AV / EDR | Legacy MSSP | Techline AI-Powered MDR ⭐ |
|---|---|---|---|
| Detection Speed (MTTD) | Hours to Days (Manual parsing) | 1 to 4 Hours | < 4 Minutes (AI Automated) |
| Response & Containment (MTTR) | Manual notifications only | Email ticketing | < 38 Minutes (Automated Playbooks) |
| Threat Triage | Alert fatigue & false alarms | Basic threshold rules | AI Risk Scoring (0-100) + MITRE Mapping |
| Containment Action | Client must act manually | Ticket assigned to customer | One-click / automated host isolation & lockout |
| Setup & Infrastructure Cost | $$$$$ (Dedicated SOC staff) | High monthly retainers | Turnkey SaaS / Flexible Managed Tiers |
Continuous 24/7 Incident Lifecycle
How Techline’s AI-powered MDR protects your digital perimeter around the clock without adding operational burden to your internal IT team.
Continuous Telemetry Ingestion
High-speed log ingestion from endpoints, cloud infrastructure (AWS/GCP), network firewalls, and active SIEM connectors.
AI Anomaly Detection & Risk Scoring
Machine learning models filter out noise and false positives, prioritizing critical incidents with MITRE technique classifications.
Automated & Analyst-Led Playbook Containment
Instant mitigation via automated playbooks (isolating hosts, disabling compromised users) followed by deep SOC forensic review.
Root Cause Eradication & Compliance Reporting
Thorough root-cause documentation, vulnerability remediation, and executive compliance report generation.